Local timeline
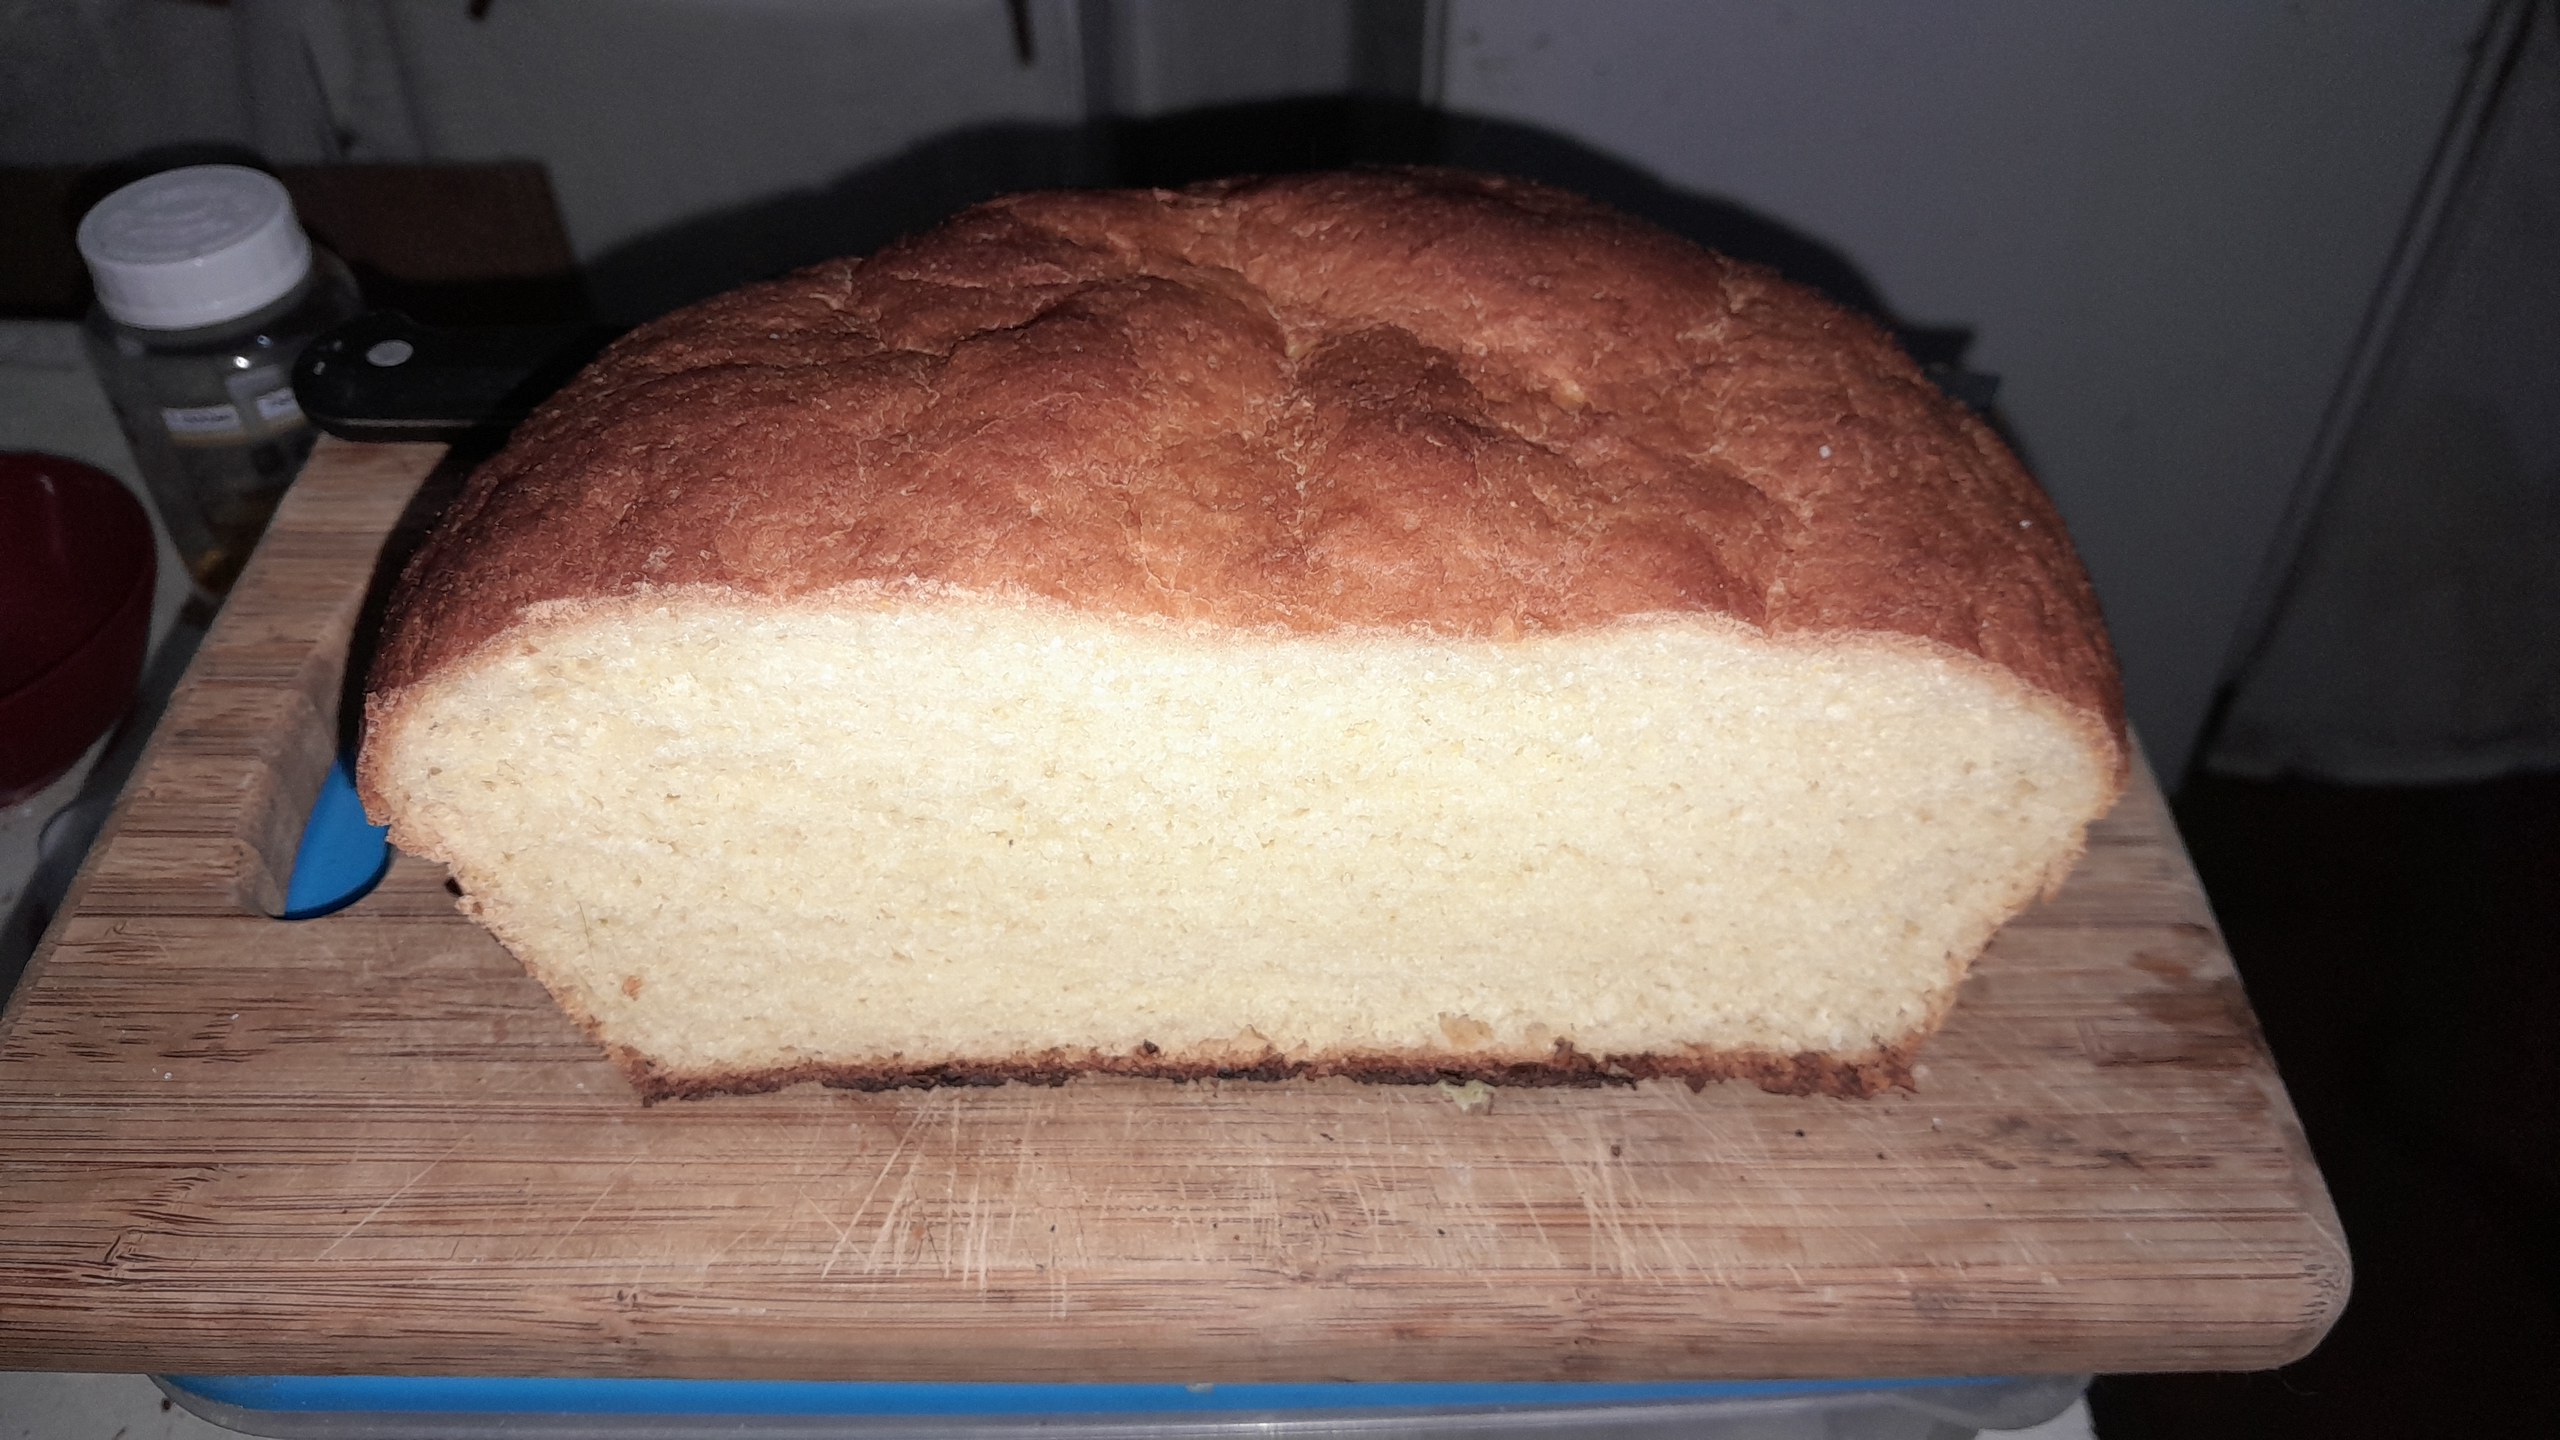
@xenotar @elias@rebel.ar @santiago@mastodon.uy @francois #pantodon Uma foto dele cortado para ver como é o miolo. A textura e o sabor ficaram muito bons.
Durante a ditadura militar o Brasil ficou inadimplente após a 1a crise do petróleo e para poupar divisas o ditador Geisel criou o "pão composto" que usava essa mistura trigo:mandioca:milho para reduzir as importações de trigo, era um "pão dágua" de padaria. Durante anos foi produzido e apreciado.
@HiMYSYeD@mstdn.ca @stesnac@snac.bsd.cafe sure! I’ll send you an invite as soon as I’ll be at computer (less than one hour)
@jack_daniel@mastodon.social @SteveBellovin@infosec.exchange My parents got married in 1949, and I believe the Singer was a model from a later year. Unfortunately, when they passed away in 1977, my sister kept the machine but soon sold it. It was a very sturdy machine. My mother had an electric one but rarely used it, preferring the treadle machine.
I love # 4 🤣🤣🤣🤣🤣
That said, yes, this AI thing is ridiculous and going to far.
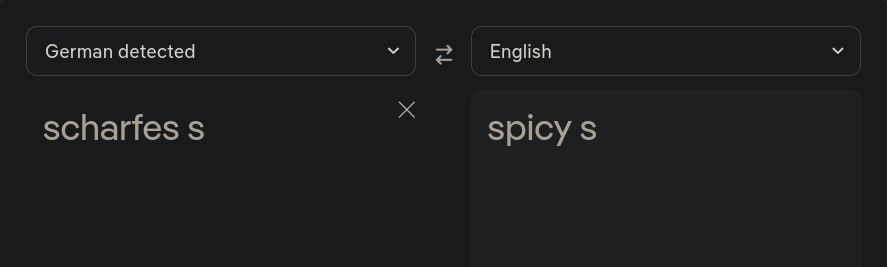
My son was looking for an english translation the other day and this is what he got !
(if you don't speak German, scharfes S is this letter: ß )
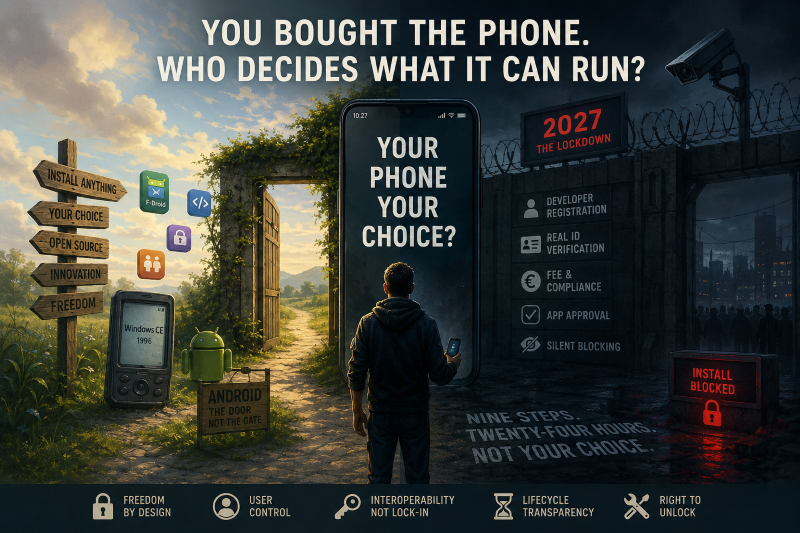
„The 2027 lockdown
In August 2025, Google announced that every Android developer must register centrally with the company before their software can be installed on any certified device. Not just Play Store apps – all apps. Apps on F-Droid. Apps a hobbyist wrote for themselves. An app you send to a friend.
Registration means a fee, Google’s terms, government ID, evidence of your private signing key, and every application identifier you will ever use. Refuse, and your software is silently blocked on every Android device on Earth.“
 @pirates@europeanpirates.eu
How we went from installing anything to asking permission – and why 2027 is the deadline
Thirty years ago, a pocket computer was a computer. Today it is a vending machine that occasionally lets you make calls.
That is not nostalgia. It is a shift that happened in front of us, one convenience at a time, and the final step is scheduled.
Stick with us; we do have a solution; it just isn’t what you expect.
Ancient times: the .cab and the .exe
Windows CE arrived in 1996, and its successors, from Pocket PC through Windows Mobile 6, governed the handheld world for a decade. The rules were the rules of a real computer. If you had a program compiled for your device’s processor, you ran it. You copied an .exe over. You double-tapped a .cab installer. Nobody’s permission was involved.
The same happens now with the switch to Apple Silicon for macOS, and Windows 11 on ARM versus the ‘good old’ x86, of Intel origin.
That is worked around with emulation in recent years, that wasn’t one of the options in ‘99.
The friction of that era was honest: you had to know whether your device was ARM, MIPS, or SH3, because the wrong binary would not run. That is a limit imposed by physics, not by a company deciding what you are allowed to want.
That distinction matters more than anything else in this article.
Android: the store as convenience
Android softened the assumption of knowledge without abandoning it. The Play Store was the easy path – one tap, curated, updated automatically. But it was a path, not a gate. Behind a settings toggle, you could install a pre-packaged .apk Android Package format file, from anywhere: a developer’s own site, a repository like F-Droid, a file a friend sent you.
That is what a healthy platform looks like. A default for the ninety-nine percent who want convenience, and a door for everyone else: the researcher, the activist, the tinkerer whose app was pulled from their country’s store for political reasons.
The door was not an oversight. It was the promise that distinguished Android from the iPhone, and millions chose Android because of it.
2026: the platforms swap places
Apple’s phone launched in 2007 with no third-party native apps at all – Jobs’ answer was web apps, and that channel never went away, because it was the one Apple could not fully police. But the rule was never “you must use our store.” It was no code runs on this device that we have not reviewed: no interpreters, no rival browser engines. Not a distribution policy: a policy about what the machine in your pocket is permitted to think.
Which makes the present moment the twist worth sitting with. The closed platform is being pried open by law while the open one is being closed by decree.
The Digital Markets Act forced Apple to permit alternative app marketplaces in the EU. In April 2025, the Commission issued its first DMA fine – €500 million – because Apple blocked developers from telling their own customers about cheaper offers elsewhere. Apple is appealing. Alternative stores now exist and work, though apps still pass through Apple’s “notarisation.” Imperfect and contested, but moving toward the user.
Google is moving the other way.
The 2027 lockdown
In August 2025, Google announced that every Android developer must register centrally with the company before their software can be installed on any certified device. Not just Play Store apps – all apps. Apps on F-Droid. Apps a hobbyist wrote for themselves. An app you send to a friend.
Registration means a fee, Google’s terms, government ID, evidence of your private signing key, and every application identifier you will ever use. Refuse, and your software is silently blocked on every Android device on Earth.
The rollout begins 30 September 2026 in Brazil, Indonesia, Singapore and Thailand. Global enforcement follows in 2027 – roughly five months from now – via a silent update to hardware people already own.
Google says power users can still install unverified apps. In practice: tap the build number seven times, dismiss warnings, enter your PIN, restart, wait twenty-four hours, return, dismiss more warnings, confirm again. Nine steps and a cooling-off period to install software on a device you paid for. And the escape hatch runs through Google Play Services rather than the operating system – so Google can narrow or remove it at any time, with no OS update and nobody’s consent.
F-Droid calls it an existential threat. The EFF calls app gatekeeping “an ever-expanding pathway to internet censorship.” Seventy-one organizations from twenty-three countries have signed an open letter against it.
The nanny arrives with good intentions
None of this began in bad faith.
As computing spread beyond the people who built it, the industry started protecting users from their own mistakes – sensible defaults, sandboxed applications, confirmation before destructive actions. That is why computers became usable by everyone.
But protection ratchets. Every safeguard that cannot be switched off encodes a judgment that the user is not competent to decide, and that judgment never expires. The warning becomes a scare screen. The scare screen becomes a twenty-four-hour wait. The wait becomes a registry.
And the logic does not stop at apps. More and more policies are being drafted and pushed forward to better protect online users. But once protection becomes a reason to remove individual control, the question is no longer limited to what software we may install. It becomes a question of who gets to decide what we may communicate, access, or create.
Europe is living the same pattern. Since 9 July 2026, Chat Control 1.0 is in force again: private messages may be scanned with no warrant and no suspicion, to protect children. Patrick Breyer’s objection is not that children need no protection – it is that indiscriminate scanning is a cheap substitute for the targeted work that would actually protect them. That is what #NeverTheNanny names.
And here the child-protection framing hides its own answer. Children lack capacity. Their guardians do not. A child’s incapacity is real, and it is answered by named adults accountable for that particular child – responsibility delegated to a parent, a grandparent, a teacher. The nanny relegates it instead: upward, to a state or a platform with no relationship to the child, and then applies the machinery to everyone. Chat Control scans every message precisely because it has no route to any actual guardian. It substitutes for a relationship the system never bothered to model.
Build the route and the blanket becomes unnecessary. FEP-633c, a guardianship proposal in draft for the Fediverse, is the existing proof — notable mostly for what it refuses to do. It does not scan for content. It does not verify anyone’s age or identity. Between adults, nothing changes at all. And it is built to end, because children grow up.
That is the distinction in one line. A guardian is specific, consented, accountable, and temporary. A nanny is universal, imposed, anonymous, and permanent — and an adult who never lacked capacity needs neither.
A protection you are not permitted to decline is not a protection.
Google’s registry is the nanny, one layer down the stack. Malware is real; the response is to fingerprint every developer on Earth, including the teenager who has never shipped anything to anyone, rather than pursue the people actually distributing it. Indiscriminate, because indiscriminate is cheaper. Note the vocabulary Google uses: power users may still install unverified apps. There is the protected majority, and a deviant class who want control over their own property and must prove they deserve it. Nobody in that framing is simply an owner.
Nor does the mechanism care about intent. A registry of everyone permitted to write software for four billion devices – held by one company with a documented record of complying when authoritarian governments demand app removals – is infrastructure that will be leaned on. And “it’s just $25 and some paperwork” answers for a developer in California with a credit card and a driver’s license. It does not answer for a student in Lagos, a dissident in Myanmar, or a volunteer maintaining a community health app.
Updates give. Updates should not take.
Nobody objects to software improving after purchase. But the channel that delivers features can also withdraw them, and we have accepted an arrangement where only one party may use it.
A device that can be made worse, remotely, after purchase, by a party you cannot negotiate with, was never fully sold to you. In software, this is called a rug pull – and there, at least, you could switch to a competitor. In hardware, it is a fait accompli.
The same fight as Stop Killing Games
In January 2026, 1.29 million Europeans signed the Stop Destroying Videogames initiative, asking that games they bought remain playable after the publisher switches off the servers. On 16 June, the Commission answered: no legislation, citing copyright constraints, offering a voluntary code of conduct instead. Organizers are now aiming at the Digital Fairness Act, expected in Q4 2026.
The European Pirates have already argued this was never really about games – it is a debate about digital rights, and the Commission’s refusal left the underlying question untouched.
Same question: what did you actually buy?
You cannot answer that about a phone whose ability to run software may be revoked by a policy update, or about a game that evaporates on a date nobody disclosed. Both were presented as ownership and delivered as a revocable license, with the terms of revocation withheld at the point of sale.
What we ask for
Not a ban on app stores. Stores are useful, and most people should keep using them.
Sideloading as a right, not a tolerance. Owners must be able to install software of their choosing, including from anonymous developers – and that guarantee must live in the operating system, not in a proprietary service the vendor can revise unilaterally.
No retroactive removal of capability. A function your device shipped with cannot be withdrawn by update. If it can be taken away, it was rented, and the price should have said so.
Lifecycle disclosure before purchase. Guaranteed years of security updates, guaranteed years of server operation, and what happens after. On the box, not in the terms.
Interoperability by default. No blocking rival browser engines, runtimes, or stores in the name of “integrity.”
The right to unlock. A device you have finished paying for should accept the operating system you choose.
A general-purpose computer that asks permission before it computes is not a computer. It is a terminal, and you are renting it. The same enclosure is being attempted on the network itself – which is why we say Stop Killing the Internet, and why the deadline on your phone deserves attention now rather than in 2027.
Contact your MEP. Contact your national regulator. Tell them a European citizen should not need a California corporation’s signature to run a program they wrote themselves.
Sources: Keep Android Open · Android developer verification · F-Droid on Google’s registration decree · EFF, application gatekeeping and censorship · Commission DMA proceedings against Apple · Apple, distribution in the EU · Commission response to Stop Destroying Videogames · Digital Fairness Act legislative train · Googles ‘power users‘ rebuttal
@erinaceus@chaos.social
Of course, you can have both and link between them.
And yes, of course, I'd vote for the opening hours on her website :)
@daisy@littleone.littlefedi.social @jeypawlik@comicscamp.club
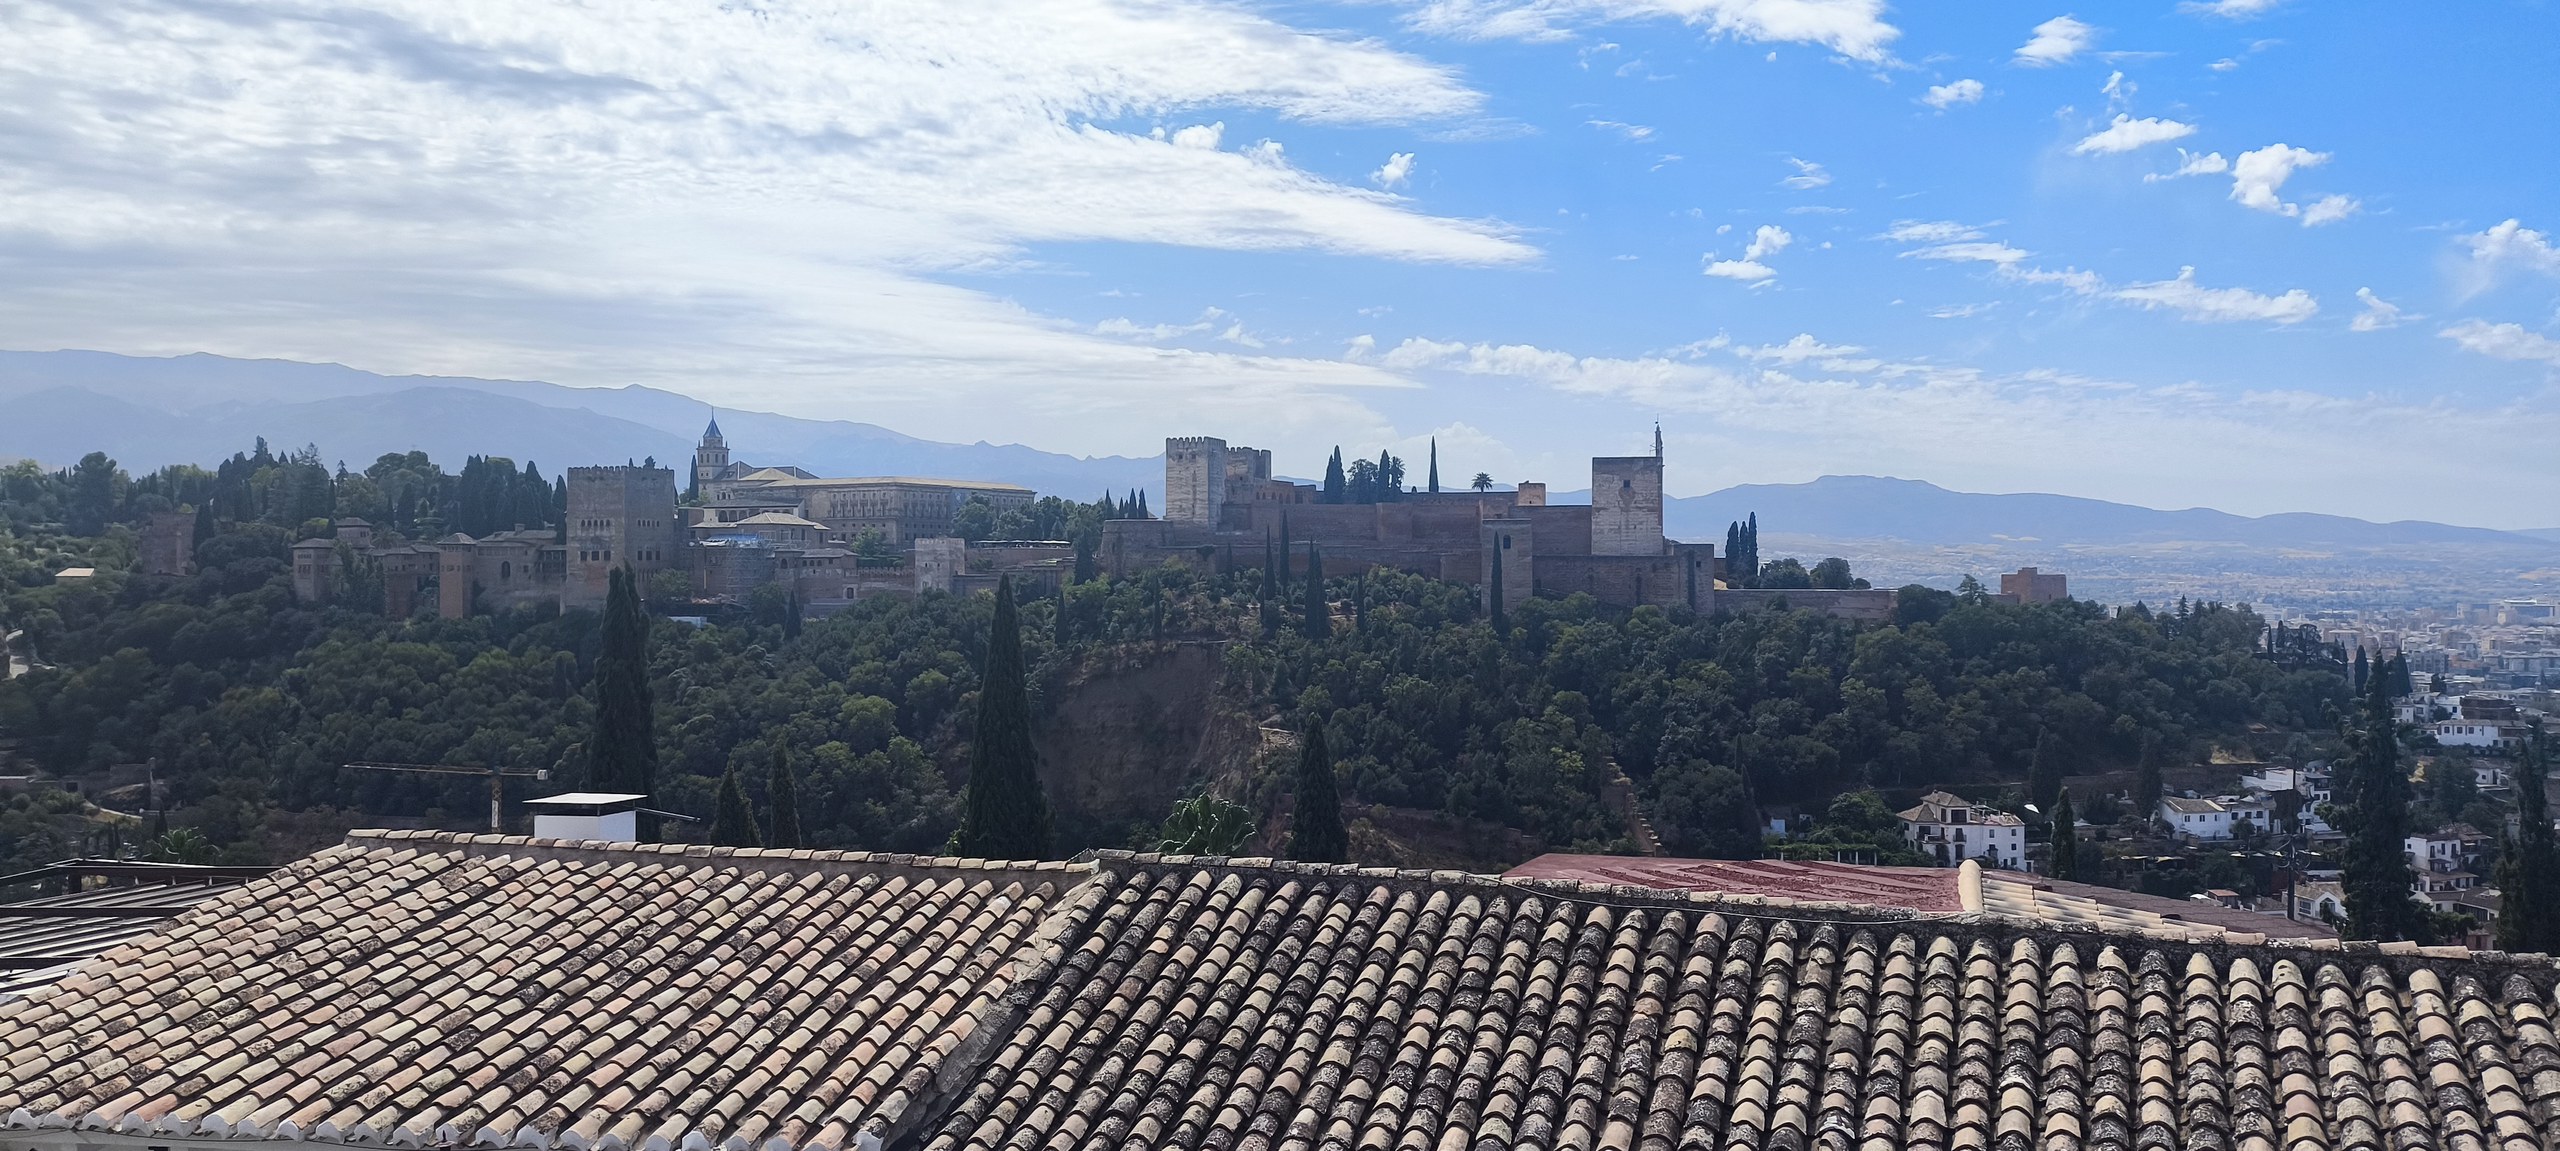
See you soon dear Granada ❤️
"Dale limosna mujer pues no hay peor condena que ser ciego en Granada"
@fasnix
Yes, one of my favorite Restaurants stays only on Instagram for a while now, too. It drives me nuts not even being able to see the menu or changed opening hours. I even reserved them a nice Mastodon account on their local city instance but they prefer now to update their opening hours only on Google maps... 🤷
@erinaceus@chaos.social @jeypawlik@comicscamp.club
@daisy @erinaceus@chaos.social @jeypawlik@comicscamp.club
Tomorrow I'll have a meeting with a person, who has her own cafe, not far from me.
She did a kickstarter campaign to raise some money and promoted it only via her Instagram (as far as I found out).
Now, she still does only use IG (via a friend, who does it for her ...).
That comic comes at the right time, as I want to try to convince her to at least get an account in the fediverse additionally, in order to build a local community.
Reasoning against IG is difficult, however I want to try it, as far as I know, she doesn't own her own webspace (website), I hope I can convince her about the advantages of one.
@daisy
„Littlefedi is for me not another mastodon but something special with this blog integration. Placing it far on the bottom looks weird to me and maybe logic for people taking littlefedi as a simple substitute for mastodon instead of a fedi-blog-system, too.“
You're right and that's one point, what makes littlefedi special for me as well :)
littlefedi is much more awesome than mastodon!
I was never on Instagram for even more reasons, but I get why people ="everyone" want it on Instagram. If your question was serious:
- it's not about a website it's about one universal all day used app
- they still think it's a community and it's great to be where cool people are and sharing the same space (like an exclusive club)
- it's easier for them (being in the Instagram app all day) to like, share and engage
- any serious account or obvious advantage kind of justifies their Instagram addiction
- it's just what everyone does, why wouldn't you make it easy for everyone, too?
Software updates
Update your software on all your platforms regularly
This is the golden rule.
- We often do it in a work environment and get paid for that
- We do it for ourselves because it is good for our devices.
- We are careful doing it on our devices which can be bricked remotely by the factory (TV's treadmills trainers)
- We install piehole and other ad blackholes to protect our devices from pesky ads
- There are so many repositories to follow
- Auto updates are stupid, IMHO, even for workstations
- On servers with PHP, we need manual granular tested updates, if we used PHP (old version) because we are slow to implement PHP (new major version)
Manual updates can be a pain
What can happen?
We forget one or two full manual updates
I've just had to do this
$ sudo ./Ventoy2Disk.sh -g -u /dev/sdx
  Ventoy: 1.1.17  x86_64
  longpanda admin@ventoy.net
  https://www.ventoy.net
Upgrade operation is safe, all the data in the 1st partition (iso files and other) will be unchanged!
Update Ventoy 1.1.12 ===> 1.1.17 Continue? (y/n) y
esp partition processing ...
update esp partition attribute
Update Ventoy on /dev/sdc successfully finished.
Did I forget something else?
Probably. Is it critical?
Lets see
$ ~/bin/yt-dlp -U
 Current version: stable@2026.07.04 from yt-dlp/yt-dlp
 Latest version: stable@2026.08.19 from yt-dlp/yt-dlp
 Current Build Hash: 495be29ff4d9d4e9be7eabdfef225221e5d5282e77f2f505abc6dca80349f3fd
 Updating to stable@2026.08.19 from yt-dlp/yt-dlp ...
 Updated yt-dlp to stable@2026.08.19 from yt-dlp/yt-dlp
It was not critical, but important none the less
Happy updating!
Sources
https://github.com/yt-dlp/yt-dlp/blob/master/README.md#installation
#programming #infosec #updates #Linux #Android #repositories #BSD
@fasnix @stefano I use the settings at the beginning only so often till everything is as expected - in my best case scenario this means one time completely from the beginning to the top. That's how I do it with every new service/app/... And going from the top to the bottom anyway the order is nothing that even interests me...
Later I would visit the settings only in the rare circumstances it's really necessary. There is the table of content all I really needed.
But if there would have to be a change for the order, in that case I would group those settings which are likely getting to change later more often to the top. And place those who are most likely a one time thing at the bottom. Combined with a "search settings" option.
I guess this would most likely result in a completely different order than suggested from you.
If I would somehow think about grouping and ordering those in a somehow "most logic" for "most people" I would still make differences of your suggestions, but I don't know if it really makes sense everyone here moves now around different points some steps more up or down.
I like having the blog close to the profile, because it's a kind of logic to start with the basics for the service(s) and in my point of view they go together and are one point I like about littlefedi and separates it from e.g. mastodon. Littlefedi is for me not another mastodon but something special with this blog integration. Placing it far on the bottom looks weird to me and maybe logic for people taking littlefedi as a simple substitute for mastodon instead of a fedi-blog-system, too.
So for my case. If anything would improve the settings order for me any further: a settings search option - but in general I'm fine with any order.
I would just keep the blog option further above because it's one of the USPs of littlefedi for me and goes together with the profile...
But in general everything my beloved little computer people decide is really fine for me there.
P.S. Only here I'm using the settings way more often than normal because of the testing. But this wouldn't be the case in a pure normal user usage.
@stefano
Good morning,
I understand that the order on the settings page may not be of highest priority and that's totally fine with me.
However, I wonder how the order came into reality in the first place?
Specifically, why the "Blog"-section comes first, right after the - splitted, imho - "Profile"-setting?
May I suggest a slightly different order / hierarchy?
Profile (Display Name, Bio, Avatar, Header)
Language
Posting
Automatic Post Pruning
Privacy
Timeline
Hashtags
Post filters
Notifications
Email Notifications
Push Notifications
Appearance
Custom CSS
Blog
Blog appearance
Security
Your data
Account
Instance Info
Account Migration
--
What do the other instance user think?
@SteveBellovin@infosec.exchange @jack_daniel@mastodon.social My mother had one of those machines; my father used it to sew fishing bags and canvas satchels. I learned how to use it and would make small items, like altering jeans to keep up with the latest trends. I never really took to modern machines.
@elias@rebel.ar @santiago@mastodon.uy @francois
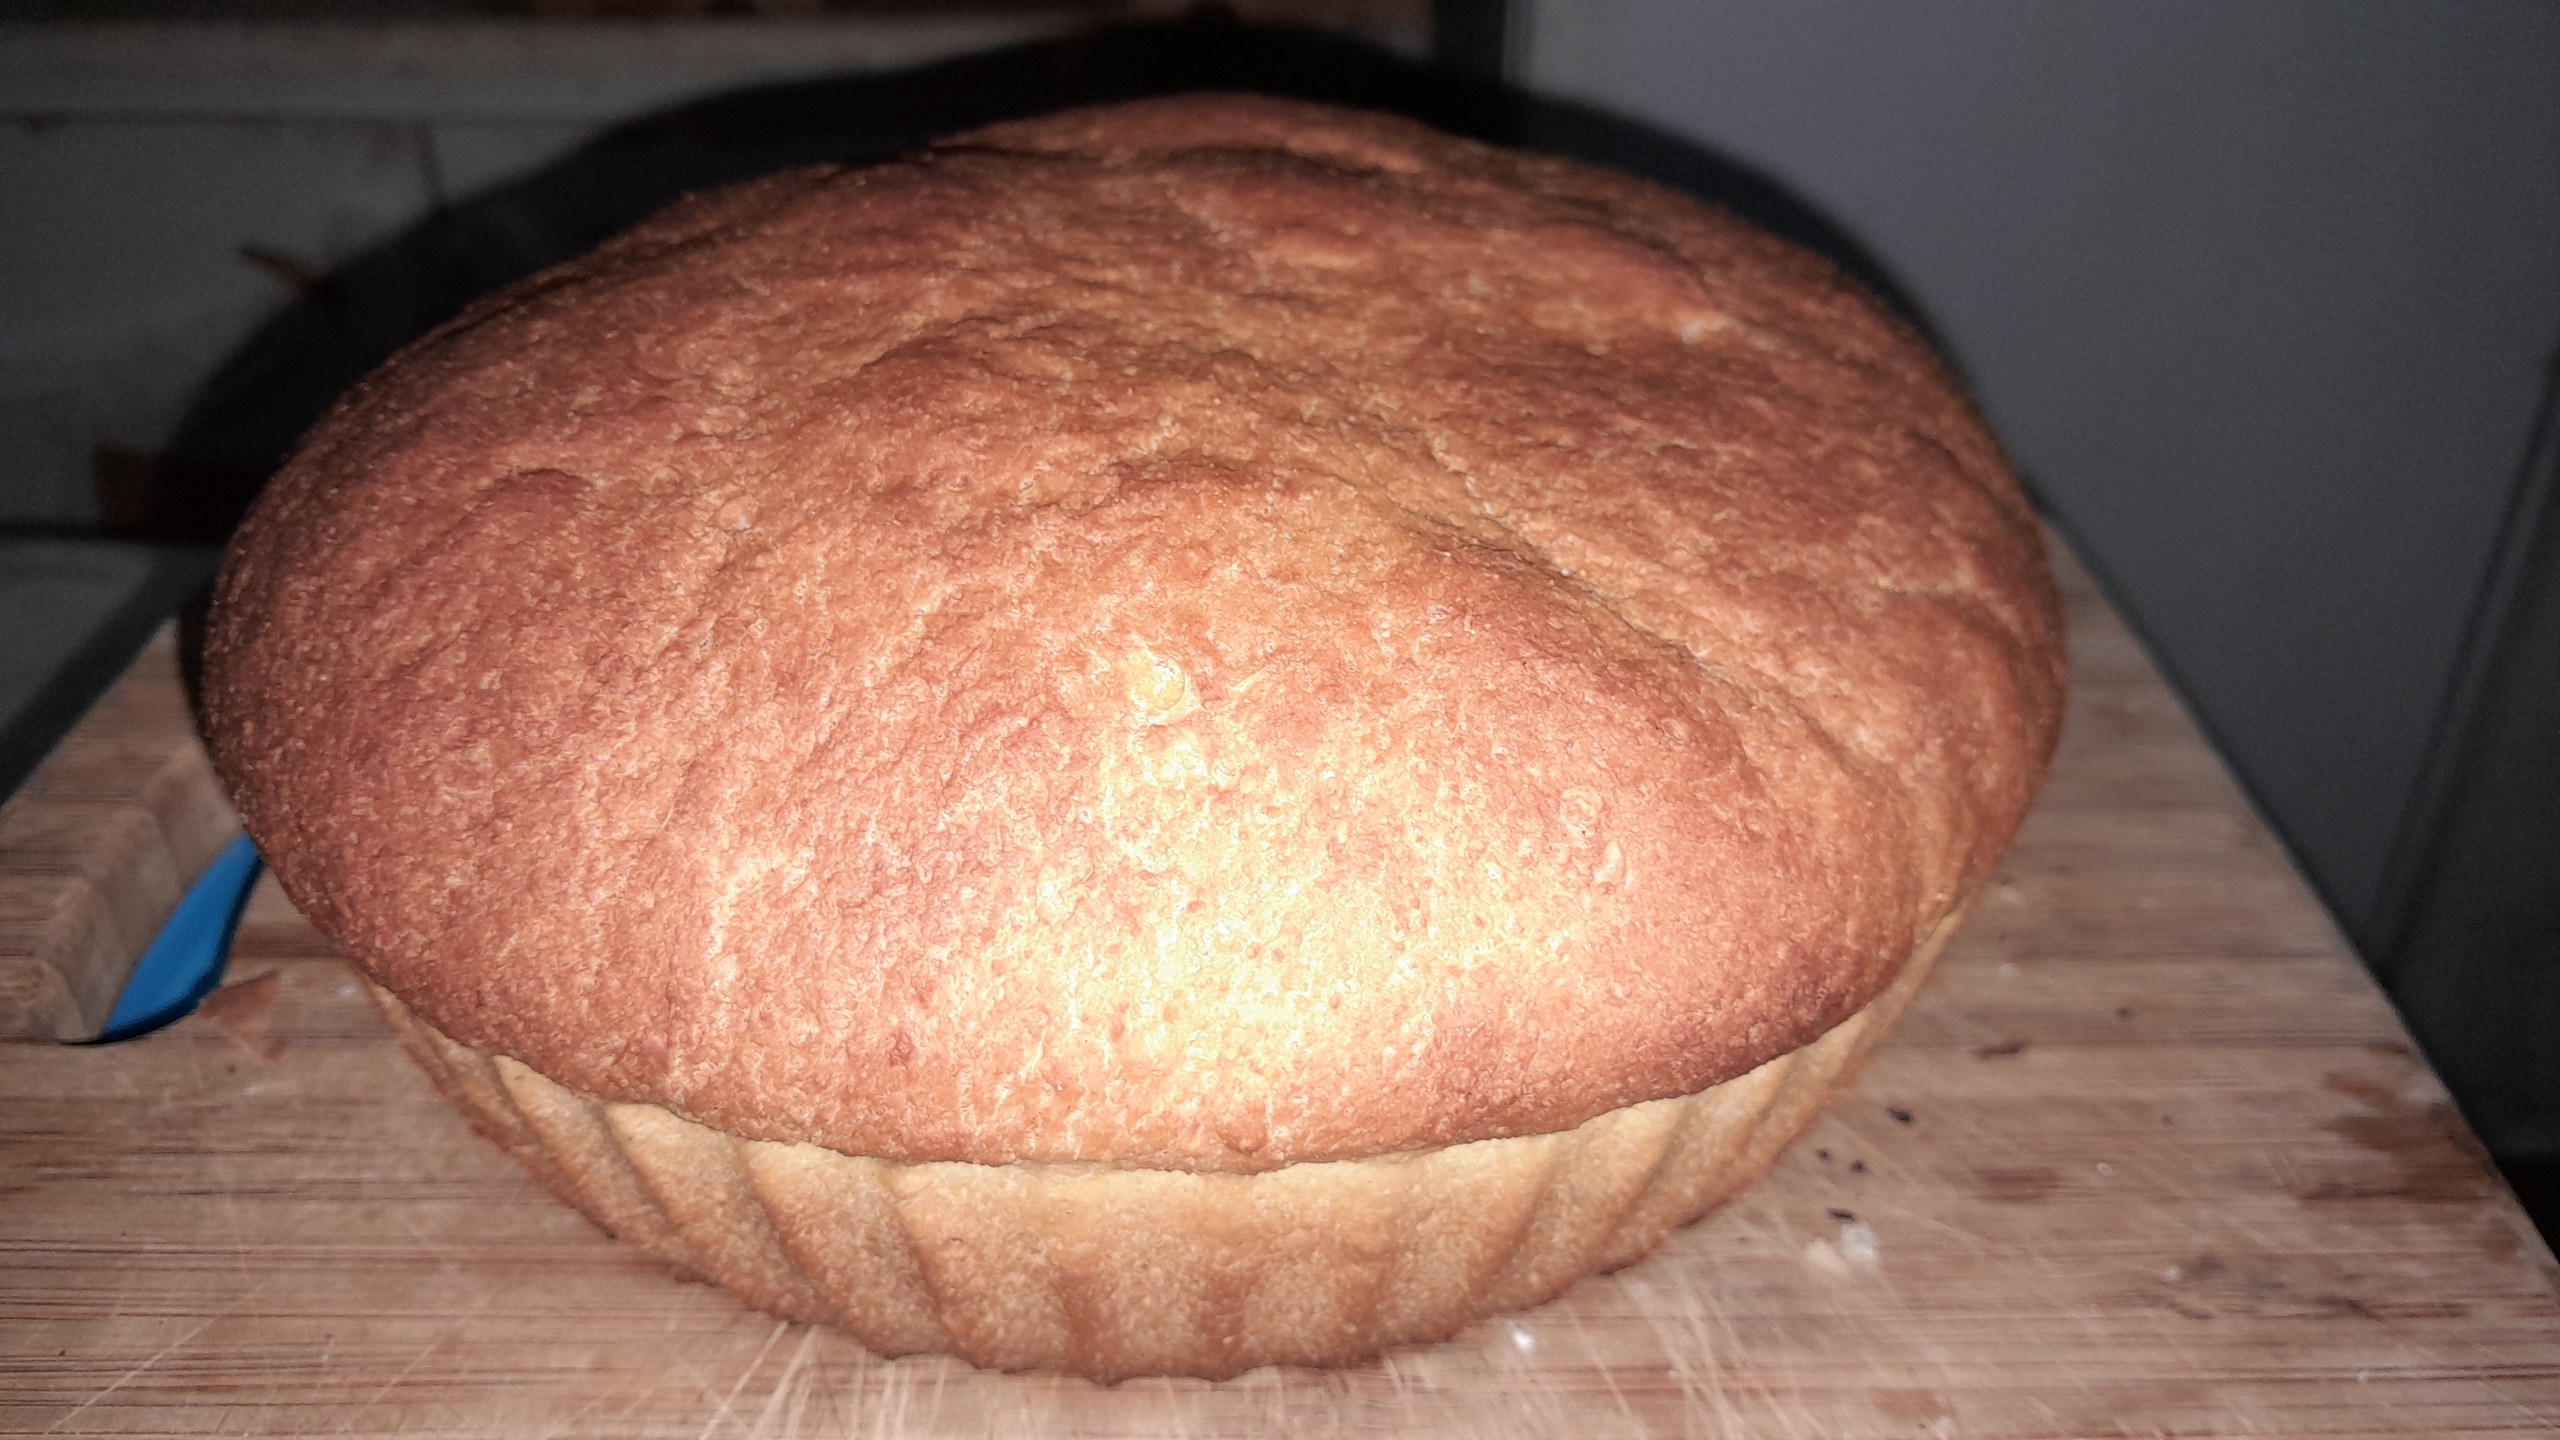
#pantodon de hoje,
Acaba de sair do forno.
Primeira tentativa com esta mistura usando farinha de milho
2 xícaras de farinha de trigo, ~1 xícara de purê de mandioca, 1/2 xícara de farinha de milho (fubá mimoso) e um fio de azeite de oliva