Local timeline
@fionescu@bsd.cafe
However, if I understand littlefedi's concept correctly, only the blog posts get rendered as "static pages".
There is no option to generate static pages, as e.g. the standard menu "About Me", "Interests", "Now", and so on?
Or would that be a feature that eventually will come along the roadmap of littlefedi, @stefano@littleone.littlefedi.social ?
That's a feature, Hubzilla, Friendica and the *key-family supports, what I really like.
@jti42@infosec.exchange The short version is: scope and threat surface.
littleMesh is trying to solve reachability and stable identity for nodes behind NAT, not to build a global discovery system.
For a DHT, the main objection was that it would introduce a whole new class of problems: replication, bootstrapping, poisoning resistance, abuse handling, consistency/consensus questions, etc. And it still would not remove the need for DNS/HTTPS when interoperating with ordinary ActivityPub servers, so the added complexity did not buy us much for the actual problem we were trying to solve.
The directory was intentionally kept much narrower. It is an authority for human-readable aliases and signed reachability information, not an index of users or content. The node identity remains self-certifying, and the directory cannot impersonate it.
Directory federation or a global view was not so much rejected forever as deliberately left out of scope. Once directories start exchanging knowledge, you need to define cross-directory trust, namespace collisions, propagation rules, conflict handling, replay/rollback semantics, abuse controls, and what exactly a “global view” is supposed to contain.
And since the directory does not contain accounts in the first place, federating directories would still not naturally produce a global account catalogue unless we deliberately added an entirely new discovery layer.
For availability, replication is actually more interesting to us than federation: having multiple directory endpoints serving the same signed state is useful because it removes a single point of failure. That is quite different from having independent directories merge into a globally searchable namespace.
So the design bias has basically been: solve the smallest networking problem necessary, keep identity cryptographically independent of the infrastructure, and leave broader discovery to the existing Fediverse mechanisms unless there is a compelling reason to add something else later.
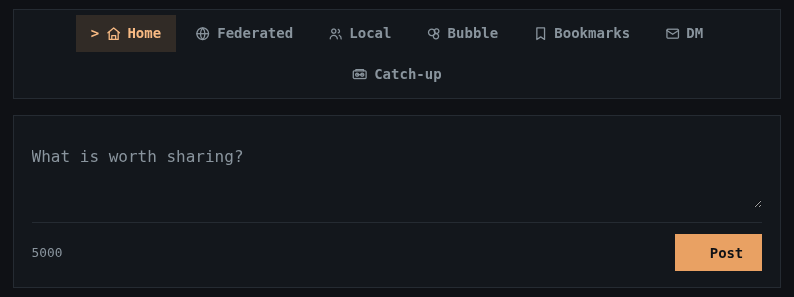
I love the new "What is worth sharing" expandable section. Much cleaner and less confusing, especially for #littlefedi newbies
@kitten_tech@fosstodon.org @ifixcoinops@retro.social it definitely could. It's already building for Android targets, even if we haven't tested it (yet)
@stefano @stefano@rpi0w.stefanomarinelli.it
Mindblowing! 🤯
I personaly think that’s what Mastodon should’ve been (I had to take down my self-hosted instance because I would have had to upgrade my VPS plan just to continue using it)
When LittleFedi will be release, it will be the start of a LOT of selfhosting instances for sure! (and the blogging hability is a striking features)
(🤔 I really need to find my rpi02 now...)
@jti42@infosec.exchange Absolutely. The documentation I mentioned is actually part of the project itself, so it will be released together with littleFedi/littleMesh once everything is ready. It includes the architecture overview, protocol details, identity model, directory design, threat model, and the reasoning behind some of the choices.
So I cannot link it publicly yet, but I definitely will once the project is released.
And yes, with one important distinction: the directory is not intended to be an account directory or a global discovery mechanism.
It only maps a readable node alias to its stable Ed25519 node ID, and a node ID to its current signed lighthouse locators. It stores no information about the accounts hosted by that node.
So enabling the directory does not create an encompassing view of users across the mesh. Account discovery remains the normal Fediverse/WebFinger/ActivityPub business once you know what you are looking for. The directory only helps you get from a human-readable mesh name to the technical node identity and then to a route to that node.
Also, at the moment directory instances do not federate or exchange their contents with each other. A node publishes to a particular directory, and a gateway/client configured for that directory knows what that directory knows. There is deliberately no DHT-like propagation or global mesh-wide index.
The Matrix comparison is interesting, though. There are certainly some similarities in separating identity, discovery, and routing concerns, although littleMesh is considerably narrower in scope: it is primarily a transport and reachability layer for ActivityPub rather than a new application-level federation protocol.
@farooqkz@bsd.cafe @themipper@mastodon.social @stefano@rpi0w.stefanomarinelli.it I know. And I was clarifying that they can happily test as the H3 is a perfect platform for this 😉
This is my very first blog post. There are many blog posts, but this one is mine.
@farooqkz@bsd.cafe @themipper@mastodon.social @stefano@rpi0w.stefanomarinelli.it I have an Orange PI PC and an Orange PI Zero. I tested littleFedi on both of them (on NetBSD).
@oscarfalcon@mastodon.social @themipper @stefano@rpi0w.stefanomarinelli.it sure, why not? We'll also make sure that it will be easy to install and maintain.
I still find this fact quite amazing, especially seeing as I have required full vps Mastodon hosting for the last 5 years. Just incredible #littlefedi can run successfully on a Pi Zero W
 @stefano
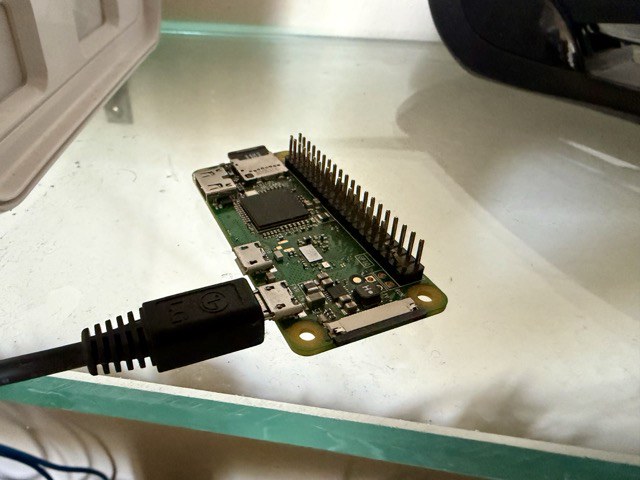
Just a little reminder on littleFedi's efficiency
The instance https://rpi0w.stefanomarinelli.it - with my user @stefano@rpi0w.stefanomarinelli.it - has been running for over a month on a Raspberry Pi Zero W powered by NetBSD.
Under normal operation, it uses 58 MB of RAM, including caches. And it shows no signs of slowness!
@themipper@mastodon.social @stefano@rpi0w.stefanomarinelli.it that will be a perfect platform for it. RAM won't be an issue and the CPU is much more performant than the original zero w
@jti42@infosec.exchange It's closer to an authenticated circuit/rendezvous relay than either a glorified STUN/TURN setup or a Kademlia-style overlay.
There is deliberately no DHT and no distributed routing/discovery protocol. A node keeps an outbound connection to one or more lighthouses. When another node wants to reach it, the lighthouse establishes a circuit between them, but the actual peer-to-peer session is end-to-end TLS inside that circuit, pinned to the nodes’ Ed25519 identities. The lighthouse therefore relays ciphertext rather than terminating the peer session.
If direct connectivity is available, peers can also discover and use the direct path, bypassing the lighthouse.
There is an optional directory, but it isn’t a DHT either. It holds signed records mapping a stable node identity to its current pinned lighthouse locators, mainly so relays can be replaced without changing the node’s identity, and to support readable aliases.
And yes, there is documentation beyond "read the code" 😉
The littleMesh documentation describes the architecture, circuit establishment, identity model, directory protocol/API, gateway, failover and trust/security model. There's also a separate littleMesh v2 identity study covering the protocol design decisions and threat model in more detail.
@mboelen people here are usually sending DMs or local only posts - and that's perfectly fine. I'm usually bookmarking everything and study them later.